
A 26-year-old Canadian man once described as one of the most consequential cybercrime threat actors of 2024 has pleaded guilty to computer fraud and conspiracy to hack and extort more than 165 organizations that used the cloud provider Snowflake. Connor Riley Moucka, of Kitchener, Ontario, also admitted to stealing call and text history records of more than 100 million AT&T customers.
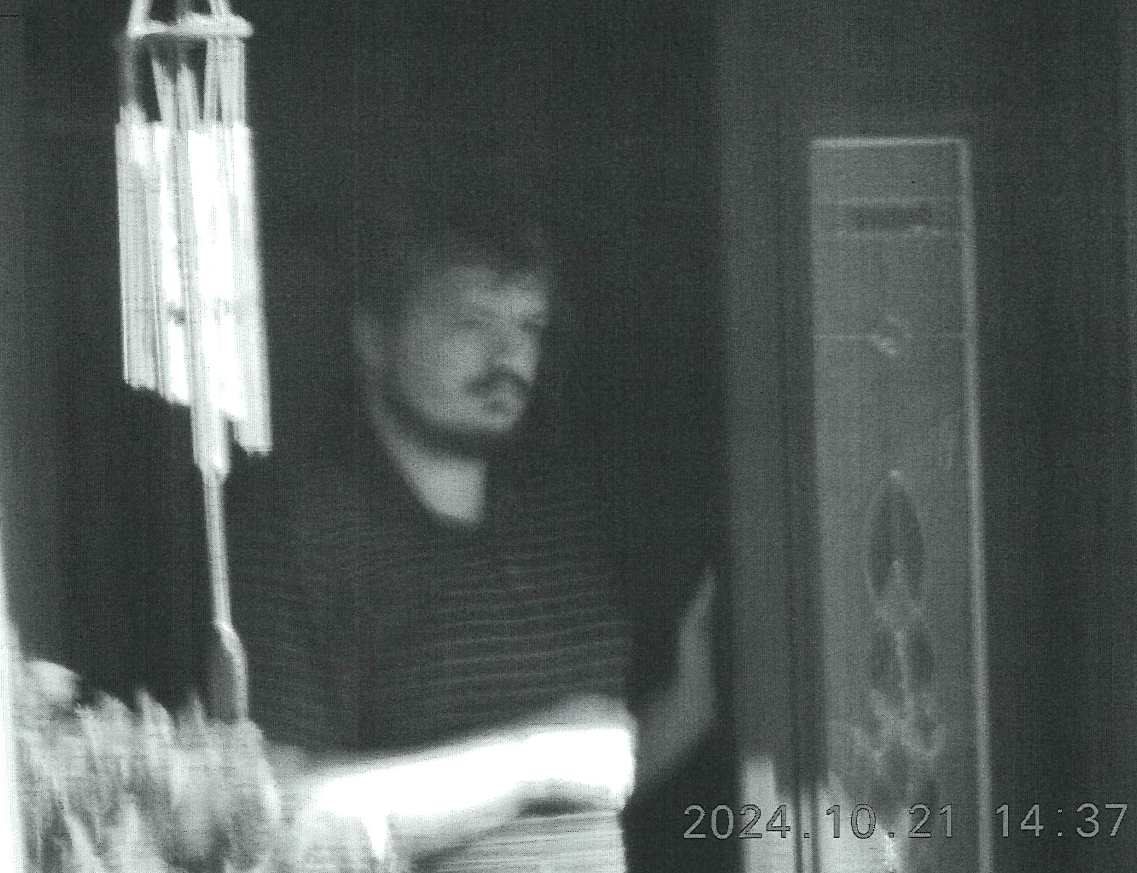
A surveillance photo of Connor Riley Moucka, a.k.a. “Judische” and “Waifu,” dated Oct 21, 2024, 9 days before Moucka’s arrest. This image was included in an affidavit filed by an investigator with the Royal Canadian Mounted Police (RCMP).
The U.S. Justice Department said between February and October 2024, Moucka and co-conspirators used stolen login credentials to steal cloud-hosted data belonging to at least 165 customers of a U.S.-based software-as-a-service company.
The hackers targeted stolen credentials for Snowflake customer accounts that did not enforce multi-factor authentication, and extorted or attempted to extort a host of well-known companies, including TicketMaster, Lending Tree, Advance Auto Parts and Neiman Marcus. Snowflake responded to the data thefts by increasing password complexity requirements and enforcing multi-factor authentication.
Moucka adopted new nicknames frequently — sometimes operating multiple identities concurrently — but two of his best-known monikers were “Judische” and “Waifu.” Judische’s admitted role in the Snowflake data thefts was first documented by KrebsOnSecurity in a September 2024 story about the overlap between Western, English-speaking cybercriminals and extremist groups that harass and extort minors into harming themselves or others.
That September 2024 story identified Judische as a software engineer from Ontario who has been involved in numerous data breaches and voice phishing attacks against U.S. companies since at least 2020. A little more than a month later, Canadian authorities arrested Moucka on a provisional warrant from the United States.
The government says Moucka and others used their unauthorized access to steal billions of sensitive customer records and download terabytes of information, “including individuals’ non-content call and text history records, banking and other financial information, payroll records, Drug Enforcement Administration (DEA) registration numbers, driver’s license numbers, passport numbers, social security numbers and other personally identifiable information. They then extorted victims by threatening to publish data online.”
Moucka also threatened and harassed government officials and security researchers who were helping to track him down. The Justice Department said the conspirators made over $2.5 million in ransom payments, and that in at least one instance, Moucka re-extorted a victim with threats of further disclosure of the victim’s stolen data.
“Moucka used the stolen data of a government officer and members of a then-former government officer’s immediate family in this re-extortion attempt,” reads a statement from the Justice Department.
One of Moucka’s admitted co-conspirators is Cameron “Kiberphant0m” Wagenius, a U.S. Army soldier who pleaded guilty in July 2025 to extorting AT&T and Verizon for their customer account data. Less than a month before Wagenius’s arrest, KrebsOnSecurity published a deep dive into Kiberphant0m’s various Telegram and Discord identities over the years, revealing how the owner of the accounts told others they were in the Army and stationed in South Korea.

One of several selfies on the Facebook page of Cameron Wagenius.
Kiberphant0m also re-extorted victims. Immediately following Moucka’s arrest, Kiberphant0m posted on hacker forums what he claimed were the AT&T call logs for then President-elect Donald Trump and for then Vice President Kamala Harris, as well schematics allegedly stolen from the U.S. National Security Agency (NSA).
Wagenius is set to be sentenced on September 3, 2026. The government says he faces a maximum penalty of 20 years in prison for conspiracy to commit wire fraud, a maximum penalty of five years in prison for extortion in relation to computer fraud, and a mandatory two-year sentence consecutive to any other prison time for aggravated identity theft.
The third alleged co-conspirator is John Erin Binns, 26, an elusive American man who fled the United States after being indicted for his admitted role in a 2021 breach at T-Mobile that exposed the personal information of at least 76 million customers.
Sources close to the investigation said Binns, also known as “IRDev” and “IntelSecrets,” was until recently incarcerated in a Turkish prison, but that he has since been released and has resurfaced online. Those sources said Binns also recently obtained Turkish citizenship, and under Turkish law a citizen cannot be extradited to a foreign country.

An image of a passport that Binns shared in an email to KrebsOnSecurity in Feb. 2023.
Moucka pleaded guilty to four criminal counts, including computer fraud, wire fraud, aggravated identity theft, and conspiracy. He is slated to be sentenced on Oct. 27 and faces a mandatory minimum penalty of two years in prison on the aggravated identity theft count, as well as a maximum penalty of 30 years in prison on the remaining counts. Ultimately, it will be up the federal judge how much time Moucka actually serves for his extensive cybercriminal rap sheet.
For an interview with Moucka prior to his arrest and a deeper look at Binns, see our original report on Moucka’s arrest.

Interesting case. It shows that attackers don’t always need sophisticated techniques—weak or reused passwords can be enough. I think more people should focus on using unique passwords for every account and enabling MFA wherever possible. Prevention is much easier than dealing with the aftermath of an account takeover
Good point. Reusing passwords is still one of the easiest ways for attackers to get in, so using a password manager and enabling MFA wherever possible makes a lot of sense.
As is always the case – your investigative skills/reporting are second to none, thank you for your ongoing work!
Re: Binns about the only plus in his so-called newfound ‘freedom’ in Turkey is he’s lucky to have been released. Hopefully he experienced some of what is described in the linked report on Human Rights violations in Turkish prisons. And as karma goes he’ll just maybe slip up and end up back there 😉
“Human rights violations in Turkey’s prisons deeply shake the concepts of social justice and human dignity. The Turkish Prisons Report (2016 – 2024), prepared by Stichting Justice Square, reveals systematic rights violations ranging from negligence that threatens the right to life of sick detainees and convicts to the inhumane conditions imposed on pregnant women and mothers with children.”
“The report particularly sheds light on the situation of sick detainees and convicts, deaths, suicides, and the conditions of ill, postpartum, and child-rearing women in prisons. The striking data and case studies presented in the report expose the dark reality of Turkey’s prisons: increasing deaths due to inadequate healthcare services, suicides under prison conditions, and worsening victimization through arbitrary and discriminatory treatment”
“It is explicitly emphasized that the systematic, discriminatory, and hate-driven practices carried out by the Erdoğan regime may constitute crimes against humanity under international law.”
https://justicesquare.org/turkish-prisons-report/
He’s prob be better off just coming back to face the music – but hey he’s made his bed, hope he has sweet dreams – NOT
It’s not cool to wish human rights violations on someone, especially when in this case John documented in the court that that was done to him via intelligence agency-led torture when he was 19 years old including an attempt to lobotomize him in a gas chamber in Germany after he refused to be recruited by the CIA. That incident is in the court documents mentioned at the end of Krebs’ 2021 article, but the word ‘bizarre’ is in there to deter curiosity.
We should all be asking about that and about why he was terrorized and threatened with false accusations before he ever moved to Turkey and why the CIA decided to have him reported as an ISIS member when he was not.
It’s not about karma.
” your investigative skills/reporting are second to none”.
True, but not editing/proof reading!
Email from you, I have been getting these for the last couple of months.
KrebsOnSecurity Mailing List . bk_at_krebsonsecurity.com chris******@duck.com
From
Reply to
bk@krebsonsecurity.com bk_at_krebsonsecurity.com chris******@duck.com
bk@krebsonsecurity.com . bk_at_krebsonsecurity.com chris******@duck.com
To
6 Aug 2026, 20:04
This may not deter others but I think all of these gentlemen should be forced to pay and MANUALLY complete all the necessary forms required for each victim to get an identity protection service in place. Once done, they can return to society and tell others.
I understand that the Libertarian Murray Rothbard suggested that they should have to pay double the total damages.
2024: “We expect that violent hackers from the [cybercrime community] will experience increasingly harsh sentences as the crackdown continues”
remember this comment and tihs one I’m writing: he will get next to nothing and none of his involvement with actual harm/extortion groups will even be considered because this is just feds working on behalf of private companies once again, same deal with big piracy cases
I am not a fan of crime or anything, but I am increasingly frustrated by the inaccurate language and sentencing guidelines. Extortion does not fit. Ransom is not accurate.
The laws and vocabulary need to be completely overhauled.
Pretty sure this is not the same as being locked in a basement (ransom) or getting beaten up behind a bar with brass knuckles (extortion). Crime? Yup. VIOLENT in its way? Alright. But experienced totally differently by the victim and little in common with the other sort of perpetrator. Sort of feel the ones that make you psychologically and physically fear every moment are not the same as the ones that simply download a file and dump hundreds of thousands of people whom were really not so singled out, and deserve different language and results in court.
“Extortion does not fit.” Says you? Lol get a job redefining things then.
Siri, let Maily’s most recent installer on the iOS version of the app store know to move their right hand down a tad on the phone. Thanks.
Gemini, let Google Play know to let Maily’s installers from March 30 know to move their hands a tad to the right, and then tap a bit further right on the Gboard keyboard. Make sure this is with the emoticon mode off. Now tap slightly higher on those keys for the next 72 hours… Thank you.
Every time you write ‘we’ with regards to your site, I get confused. Are you referring to you and your wife? Do you have a staff at all? What does it mean? I thought it was just your personal professional blog. Is there a we??
Sun and fun for some.
Guessing Moucka doesn’t realise what he has to do if it’s his first time there.
Until the punishments are more severe than a slap on the wrist (a year or two locked up), these crimes will continue. I pray that President Trump or his successor will take a harsh stance on cyber crime. Depending on the amounts and the individuals / entities targeted, no punishment should be off the table, up to and including death sentences. Americans are losing their life savings and killing themselves because cyber criminals think they’re untouchable and unlikely to face any real consequences.
Maybe…. But two years locked up in 2026, and what happens afterwards, is way worse than two years locked up in 2002 (except for I guess the part where you can get minimum wage work more easily), or 2008 (where you could have still gotten a legit job in tech without much fanfare). Now you can end up like Guidry.
tf ts suppoed 2 mean bitc
apparently people with names similar to these people being busted have been having a lot of unfortunate things happening to them, like illness and traveling accidents in Thailand and whatevs. Was looking up dockets and ouch.
Weird stuff.
Our boy was just playing on the computer. Homie aint do nothing, we literally are propagating our brain-computer interfaces using the children of us citizens in their own homes on US soil.
Hi, this message is being wrote entirely involuntarily, using technology in this man that, according to the medical literature. should be lethal.
Hey cybersecurity experts, our technology is probably in many of your brains too. This is the only relevant threat model to you, everything else, is just playing on the computer.
The detail that stood out to me is how much of this Snowflake damage traced back to credentials without MFA rather than an exotic exploit. It is a useful reminder for any public data product, including sports and fixture-analysis tools like ours, that trust often depends on boring controls: account hygiene, logging, and fast revocation when something looks wrong.
From all the incidents I have seen it seems a lot of companies think cyber security is a joke. It goes both ways companies face no real penalties for not doing their due diligence on protecting their customers data.
And the malicious actors who attack these systems essentially face 0 punishment.
Now i know the difference between the two and two wrongs do not make a right. But some of the negligence that we all have mostly seen when ever a data breech has happened. is mostly due to gross negligence because risk calculus decisions or they simply do not seem to care.
We can only hope that eventually there will be harsher punishments on both ends so these things stop happening so frequently as they are.
From all the incidents I have seen it seems a lot of companies think cyber security is a joke. It goes both ways companies face no real penalties for not doing their due diligence on protecting their customers data.
And the malicious actors who attack these systems essentially face 0 punishment.
Now i know the difference between the two and two wrongs do not make a right. But some of the negligence that we all have mostly seen when ever a data breech has happened. is mostly due to gross negligence because risk calculus decisions or they simply do not seem to care.
We can only hope that eventually there will be harsher punishments on both ends so these things stop happening so frequently as they are.
Remarkable how much of this case still comes down to basics: stolen credentials from infostealer logs, pointed at accounts with no MFA. 165 victim organizations and the root cause was largely a missing second factor. The lesson keeps being relearned — phishing-resistant MFA and session hygiene are cheap insurance compared to the downstream extortion and notification costs. Thanks for tracking these prosecutions through to the guilty plea; most coverage stops at the indictment.
The inflection point in this saga was never the malware – it was the absence of MFA on what were marketed as enterprise-grade cloud accounts. 165 organizations, and the common denominator was a login page that accepted a stolen password as sufficient identity. The defensive fix was one policy toggle for most tenants, orders of magnitude cheaper than the extortion bills that followed. The fact that accounts without MFA enforcement were the targeting criteria also says the attackers did unglamorous reconnaissance at scale rather than spear-phishing their way in one by one, which is the part more organizations should internalize.