Category Archives: The Coming Storm
Conti Ransomware Group Diaries, Part II: The Office
Earlier this week, a Ukrainian security researcher leaked almost two years’ worth of internal chat logs from Conti, one of the more rapacious and ruthless ransomware gangs in operation today. Tuesday’s story examined how Conti dealt with its own internal breaches and attacks from private security firms and governments. In Part II of this series we’ll explore what it’s like to work for Conti, as described by the Conti employees themselves.
Conti Ransomware Group Diaries, Part I: Evasion
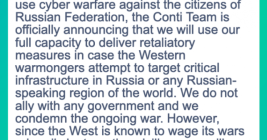
A Ukrainian security researcher this week leaked several years of internal chat logs and other sensitive data tied to Conti, an aggressive and ruthless Russian cybercrime group that focuses on deploying its ransomware to companies with more than $100 million in annual revenue. The chat logs offer a fascinating glimpse into the challenges of running a sprawling criminal enterprise with more than 100 salaried employees. The records also provide insight into how Conti has dealt with its own internal breaches and attacks from private security firms and foreign governments.
Russia Sanctions May Spark Escalating Cyber Conflict
President Biden joined European leaders this week in enacting economic sanctions against Russia in response its military invasion of Ukraine. The West has promised tougher sanctions are coming, but experts warn these will almost certainly trigger a Russian retaliation against America and its allies, which could escalate into cyber attacks on Western financial institutions and energy infrastructure.
Scary Fraud Ensues When ID Theft & Usury Collide
What’s worse than finding out that identity thieves took out a 546 percent interest payday loan in your name? How about a 900 percent interest loan? Or how about not learning of the fraudulent loan until it gets handed off to collection agents? One reader’s nightmare experience spotlights what can happen when ID thieves and hackers start targeting online payday lenders.
At Request of U.S., Russia Rounds Up 14 REvil Ransomware Affiliates
The Russian government said today it arrested 14 people accused of working for “REvil,” a particularly aggressive ransomware group that has extorted hundreds of millions of dollars from victim organizations. The Russian Federal Security Service (FSB) said the actions were taken in response to a request from U.S. officials, but many experts believe the crackdown is part of an effort to reduce tensions over Russian President Vladimir Putin’s decision to station 100,000 troops along the nation’s border with Ukraine.
‘Wormable’ Flaw Leads January 2022 Patch Tuesday
Microsoft today released updates to plug nearly 120 security holes in Windows and supported software. Six of the vulnerabilities were publicly detailed already, potentially giving attackers a head start in figuring out how to exploit them in unpatched systems. More concerning, Microsoft warns that one of the flaws fixed this month is “wormable,” meaning no human interaction would be required for an attack to spread from one vulnerable Windows box to another.
The Internet is Held Together With Spit & Baling Wire
‘Trojan Source’ Bug Threatens the Security of All Code
Virtually all compilers — programs that transform human-readable source code into computer-executable machine code — are vulnerable to an insidious attack in which an adversary can introduce targeted vulnerabilities into any software without being detected, new research released today warns. The vulnerability disclosure was coordinated with multiple organizations, some of whom are now releasing updates to address the security weakness.
How Coinbase Phishers Steal One-Time Passwords
A recent phishing campaign targeting Coinbase users shows thieves are getting cleverer about phishing one-time passwords (OTPs) needed to complete the login process. It also shows that phishers are attempting to sign up for new Coinbase accounts by the millions as part of an effort to identify email addresses that are already associated with active accounts.